IT Risk · Compliance · Audit
Give IT risk an owner.
A Managed Risk Provider (MRP) for IT risk and compliance. Rennie GRC provides ongoing risk, compliance, control and remediation oversight—giving organizations a dedicated owner for IT risk without adding another full-time role.
The Gap We Fill
IT operates the environment. Who keeps the risk work moving?
In many organizations, IT risk, control reviews, audit follow-up and compliance activities become an additional responsibility for people already focused on uptime, users, projects and security operations.
Rennie GRC works alongside the people you already have. We can coordinate with management, internal IT, your MSP, vendors and auditors while maintaining focus on risk throughout the year.
Flagship Service
Ongoing IT Risk & Compliance
A recurring relationship for organizations that need someone consistently focused on technology risk, controls, compliance and audit readiness—but do not need another full-time position.
Risk & Issue Management
Maintain a practical IT risk register, document ownership and treatment decisions, and keep remediation from disappearing after the meeting.
Controls & Evidence
Review key controls, evidence and exceptions throughout the year so audit readiness becomes an operating practice rather than a scramble.
Management Reporting
Translate technical conditions into concise risk updates, KRIs/KCIs, priorities and decisions leadership can act on.
Audit & Exam Support
Coordinate requests, evidence, responses, findings and remediation with internal auditors, external auditors and other reviewers.
Vendor & Third-Party Risk
Bring structure to vendor reviews, access, dependencies, security expectations, findings and ongoing oversight.
Resilience & Recovery
Keep backup testing, recovery objectives, DR runbooks and tabletop exercises connected to actual business requirements.
Ways To Engage
Start where your organization needs help.
Dedicated IT Risk & Compliance
Recurring support that keeps risks, controls, findings, vendors and management reporting moving throughout the year.
Explore ongoing support →ASSESSRisk & Compliance Assessments
Focused IT risk, controls, HIPAA, audit-readiness and recovery reviews with prioritized, usable findings.
Explore assessments →IMPROVERemediation & Advisory
Practical help addressing selected technology findings—directly or in coordination with your existing IT team or provider.
Explore remediation →Industries We Support
IT risk looks different in every industry.
The underlying need is the same: identify technology risk, maintain ownership, keep controls working and move remediation forward. Rennie GRC applies that approach to the requirements that matter in your environment.
Customer, Supply Chain & Operational Risk
Customer security requirements, cyber insurance, ransomware, supply-chain and vendor risk, recovery planning, and CMMC where applicable.
Controls, Examinations & Resilience
IT controls, regulatory examinations, vendor management, cybersecurity governance, audit findings, BCP/DR and ongoing risk reporting.
HIPAA, Security & Recovery
HIPAA Security Risk Assessments, ongoing risk management, remediation tracking, third-party risk, ransomware preparedness and recovery.
Assurance, Customer Trust & Licensing
SOC 2 and ISO 27001 readiness, customer security requirements, ITGCs, third-party risk, evidence management and software licensing risk.
Works With Your Existing IT
Independent IT risk support that works with your existing technology team.
Your internal IT team, MSP or technology vendors can keep operating the environment. Rennie GRC focuses on whether risks are identified, controls are effective, findings are resolved and management has the information it needs.
“Who owns IT risk and compliance between audits?”
If the answer is “IT handles it when they have time,” there may be a gap worth addressing.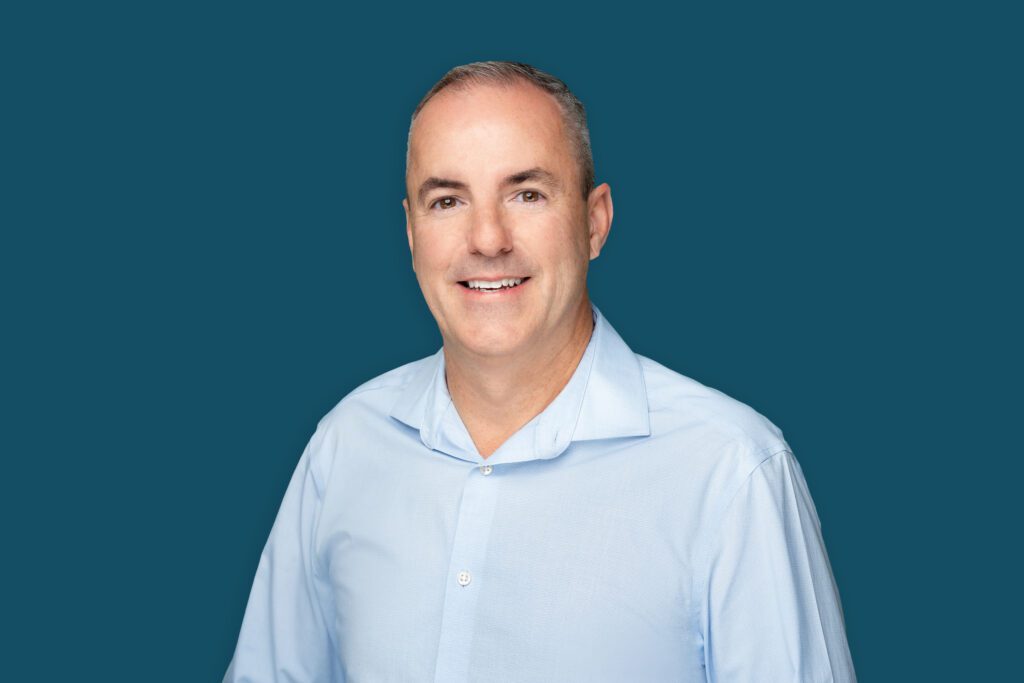
Built on Experience.
I'm Robert Rennie, founder of Rennie GRC.
I've spent more than 20 years working with business technology — from hands-on systems and infrastructure to cybersecurity, IT audit, and technology risk.
I started Rennie GRC to help organizations give IT risk, compliance and audit work sustained attention. The goal is to identify what matters, translate technical issues into business risk, keep remediation moving and give leadership a clearer view of technology risk.
Focused Expertise
Common areas we can own or support.
Start With A Conversation
Does IT risk have a dedicated owner in your organization?
Tell us how risk, compliance and audit work is handled today. We can discuss whether ongoing support, a focused assessment or targeted remediation makes sense.